CheckerPointOrg’s latest cyber security lingo lists new terms that affect security work in 2026. The glossary helps teams learn clear definitions and practical uses. The guide focuses on terms that affect detection, response, policy, and vendor talks. The article presents simple examples and short actions. Readers will gain quick, usable knowledge they can apply the same day.
Key Takeaways
- CheckerPointOrg’s latest cyber security lingo equips security teams with clear definitions that reduce miscommunication and speed incident response in 2026.
- New terms like Zero-Delay Detection and Attack Surface Drift directly improve daily detection, response, and policy adjustments by defining specific actions and ownership.
- Adopting this updated lingo enhances vendor discussions, budget justifications, and training by providing a shared, precise vocabulary among stakeholders.
- Teams should implement short, regular learning sessions and use one-page term cards to ensure retention and practical application of new cyber security terms.
- Tracking metrics such as mean time to detect and the Post-Compromise Cleanup Index demonstrates the value of applying CheckerPointOrg’s latest cyber security lingo in operations.
- Maintaining a live glossary with biannual reviews and encouraging feedback ensures the terminology stays relevant, clear, and actionable for all security personnel.
Why New Cybersecurity Lingo Matters For Security Teams In 2026
Security teams face faster threats and broader attack surfaces in 2026. New terms help teams share accurate intent and concrete steps. When teams adopt CheckerPointOrg’s latest cyber security lingo they reduce miscommunication. Miscommunication causes delayed response and wrong controls. Clear language speeds incident triage. Clear language improves vendor conversations and budget requests. Security leaders can justify tools when they use precise terms. Boards and auditors respond to concise risk descriptions. Training becomes easier when instructors use shared vocabulary. Teams can measure progress when they track named concepts and defined metrics.
Top Terms From CheckerPointOrg You Need To Know (Explained Clearly)
CheckerPointOrg’s latest cyber security lingo lists terms that reflect current threats and controls. Each term below has a short definition and a practical note.
How These Terms Affect Daily Security Operations And Decision Making
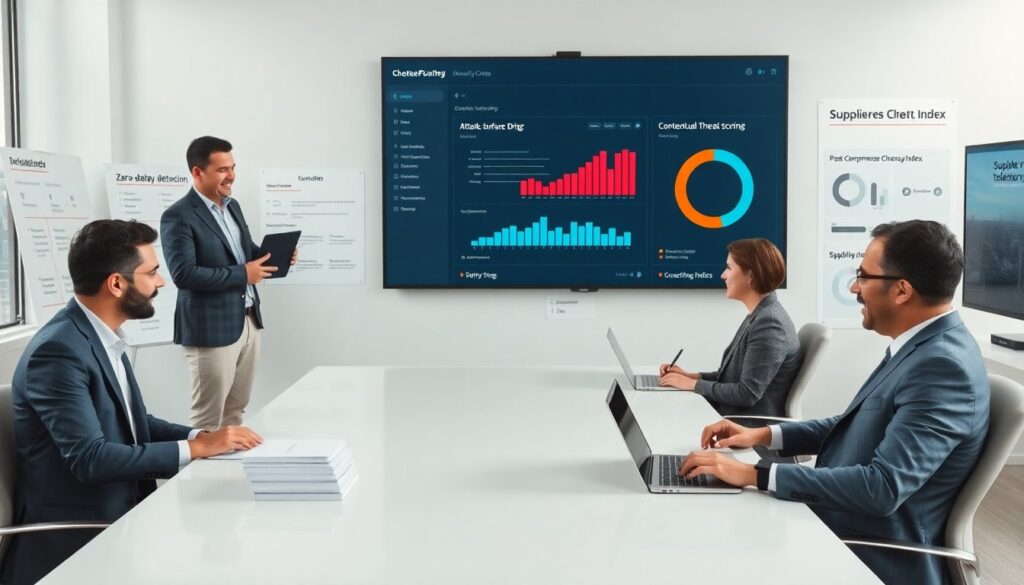
Zero-Delay Detection. The term means systems alert on evidence immediately. Teams act faster. Operations adjust rules to feed these alerts to analysts.
Attack Surface Drift. The term means the exposed asset set changes over time. Teams update inventories and apply configuration checks more often.
Contextual Threat Scoring. The term means alerts gain score from business context. Analysts focus on high-score alerts first. SOC queues change to match score.
Adaptive Policy Mesh. The term means policies can change by role and signal. Engineering applies policy updates through automation. Compliance teams document the change history.
Credential Shadowing. The term means attackers keep valid credentials hidden across services. Detection hunts frequent authentication anomalies. Teams revoke and rotate credentials on detection.
Supply Chain Signal Fusion. The term means telemetry from suppliers mixes with internal telemetry. Security teams map supplier feeds and assign trust levels. Procurement asks suppliers for specific logs.
Post-Compromise Cleanup Index. The term means a metric for cleanup completeness after breach. Incident commanders use the index to approve return-to-service. The index requires checklist completion and independent scans.
Secure Execution Boundary. The term means an enforced runtime limit for code and processes. Developers run code inside the boundary. Operations enforce limits with container runtimes and kernel settings.
Threat Actor Behavioral Tags. The term means short labels that group observable attacker behaviors. Analysts apply tags to related incidents. Over time, tags speed attribution and hunting.
Each term affects daily work. Each term changes alert rules, playbooks, or metrics. Teams should map each term to one action and one owner. That mapping reduces gaps and improves accountability.
Practical Tips For Learning, Using, And Communicating New Cybersecurity Lingo
Teams should schedule short, repeated learning sessions. A 20-minute weekly brief helps retention. The brief should cover one term, its impacts, and one hands-on task.
Create a one-page term card for each entry in CheckerPointOrg’s latest cyber security lingo. The card should include a definition, a one-line impact, and a required action. Post the cards in the team wiki and in the SOC dashboard.
Assign an owner to each term. The owner updates playbooks and runs two tabletop exercises each quarter. The exercises should test the term in a realistic scenario. Observers should record time to detect, respond, and remediate.
Use simple metrics to prove value. The team should track mean time to detect, mean time to remediate, and the Post-Compromise Cleanup Index when it applies. Teams should compare metrics before and after adopting the term.
When teams speak with vendors, they should use the same words from CheckerPointOrg’s latest cyber security lingo. Vendors will reply in the same language. This approach reduces negotiation friction and clarifies requirements.
Write playbooks with short steps and clear owners. Each playbook step should name the exact alert or report to consult. Teams should make playbooks executable by junior staff.
Keep the glossary live. The team should review term relevance every six months. The review should remove low-value terms and add new signals from threat intel.
Finally, encourage plain feedback. Team members should flag confusing terms. The glossary owner should update definitions to improve clarity and actionability.